Muse’s Real Product Test Is Whether Users Understand What They Have Authorized
Meta’s agent can keep working after its app closes. That makes clear, timely consent part of the everyday experience, not a setting users should have to decipher.
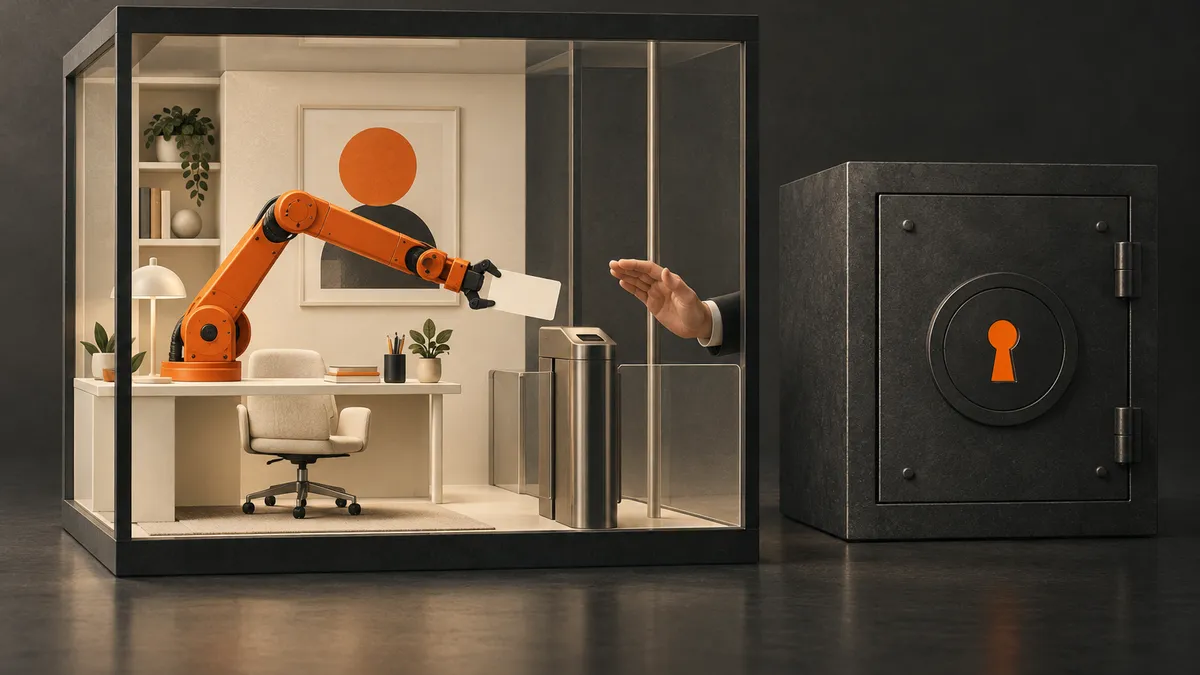
Meta introduced Muse on September 8 as a personal AI agent that can carry out tasks through connected services and a browser. The company says it runs in a dedicated cloud virtual machine, a separate computing environment, and can continue working after the user closes the app. It is beginning its rollout in the United States.
The appealing promise is relief from supervision: hand over a task and return when the work is done. But a person cannot delegate intelligently if they do not understand what the agent is allowed to do along the way. Muse’s product challenge is to make that understanding easy enough to survive ordinary use. A permission system that exists technically can still fail the person trying to rely on it.
That makes its permission system central to the product. Meta describes a separate Sentinel component that checks internet actions and seeks approval when needed, plus controls over connected apps, access scopes and revocation. The launch announcement identifies sending emails and making purchases as actions that can require user permission.
Consent should follow the consequence
The useful boundary is the change in consequence. Reading information, preparing a proposed response and sending that response are different acts from the user’s point of view. A product should make those differences visible where they matter. If the interface presents them as one undifferentiated task, the user may grant more authority than intended without ever making a conscious decision to do so.
Constant interruption is not the answer either. An assistant that asks for approval at every harmless step can make delegation feel pointless. Worse, repetitive prompts could encourage a person to click through mechanically. The better goal is selective friction: ask clearly when an action crosses a meaningful boundary, while allowing the routine steps the user has already authorized to proceed. That is a design judgment, not a count of permission dialogs.
A current control and a future promise
Meta says users can opt out of model training and that conversations and virtual-machine data will not be used for Meta ads. Separately, it plans Muse Confidential VM for later this year, with a user-held key intended to keep even Meta from accessing the environment. That future option should not be read as a property of the current launch.
Privacy promises need a clock
A future privacy feature cannot explain how a product handles information today. Users should be able to distinguish a launch capability, an available setting and a promised later feature without decoding an announcement. That distinction matters even when the roadmap is credible. A person deciding whether to connect an account has to make the decision under the conditions that apply when they connect it.
Privacy and authority also require separate explanations. Someone might be comfortable with a service processing information but unwilling to let it send messages. Another person could want broad assistance while restricting training use. Neither preference can be inferred from the other. A single impression that the product is private would be an inadequate guide to what it may do on the user’s behalf.
Associated Press coverage places Muse within Mark Zuckerberg’s broader ambition for agents that work on people’s behalf. Agentive has not tested Muse’s controls. The announcement describes how Meta intends to constrain actions; it does not independently establish how the system behaves when a task encounters a misleading page or an ambiguous instruction.
The fact that work can continue after the app closes makes the handoff especially important. Closing a window is a familiar way of ending an interaction. Here, the product’s value includes continuing beyond that moment. The interface needs to make the ongoing task understandable, including how to see its status and stop it. These are criteria for judging the experience, not claims about behavior observed in our own test.
For a hypothetical travel task, permission to search for a hotel would not necessarily express the user’s consent to book a nonrefundable room. The consequential detail would be the approval request: whether it clearly identifies the hotel, dates, total cost and cancellation terms before the purchase. A general promise of user control leaves those interaction details to be demonstrated.
In the hotel example, a useful approval would explain the relevant terms of the proposed booking before asking for a decision. A vague request to continue the travel task would leave too much interpretation to the user. The same principle applies to sending an email: the consequential object is the message and its recipients. Consent becomes meaningful when the person can understand the action being approved.
Recovery belongs in the experience too. If a person withdraws access, they need a clear account of what has stopped and what has already happened. Revoking permission cannot necessarily undo an external action. A product that explains that boundary helps the user retain a realistic sense of control. The point is not to promise perfect reversibility; it is to avoid making control seem broader than it is.
Muse should be evaluated by how confidently an ordinary person can delegate a useful task without guessing about the agent’s authority. That is a higher bar than displaying a safety component or a privacy setting in a launch announcement. It is also a more useful product ambition. The agent becomes worth keeping when people understand the handoff well enough to trust it, and can interrupt it without wondering what they have set in motion.